Ad Fraud Observatory 2019: The Mobile Assault, Click Farms, and the Official App Store Scandal
In 2019, ad fraud infiltrated official app stores with 600M+ infected downloads. The Adprodex Observatory analysis on mobile fraud.
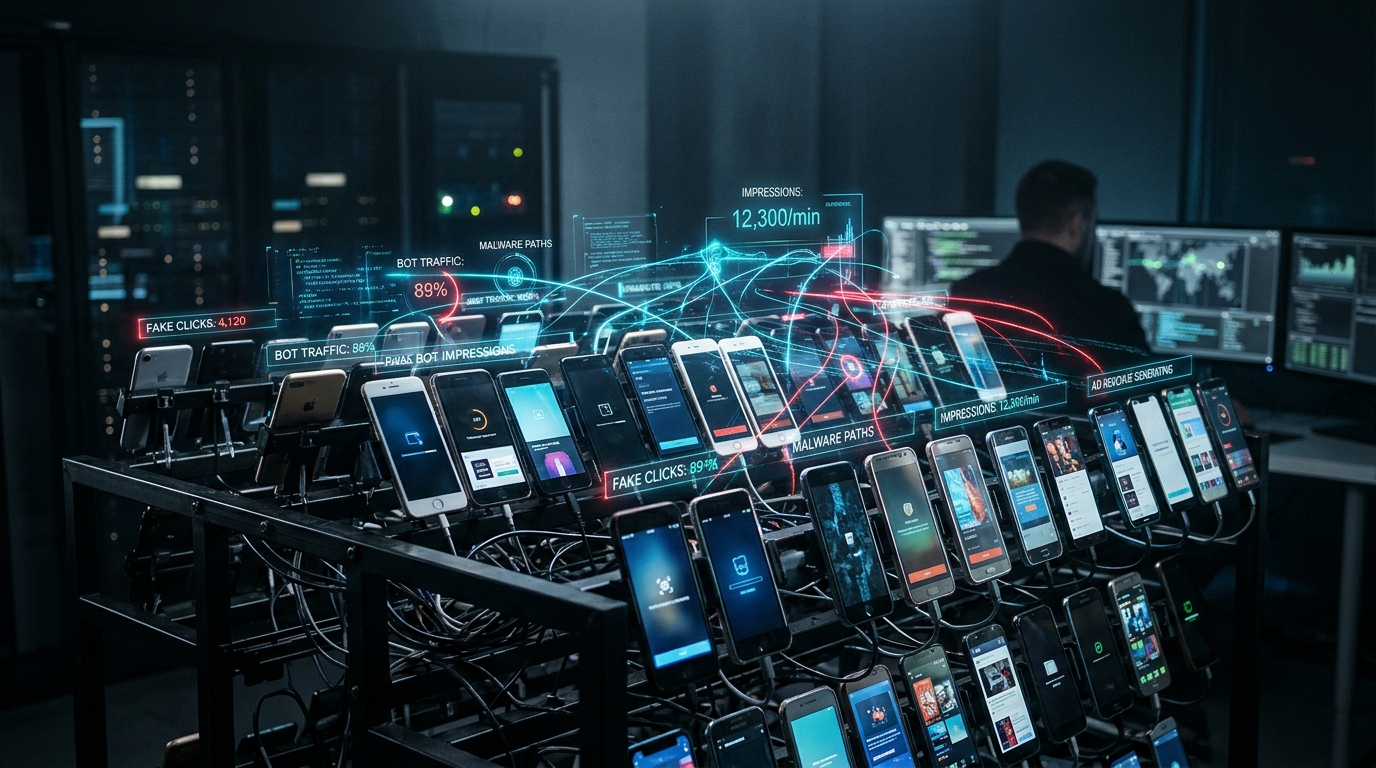
While ad fraud between 2015 and 2017 thrived primarily on desktop browsers and inside server data centers, 2019 marked the mass migration toward mobile advertising. With billions of consumers glued to their smartphone screens, cybercriminal networks turned everyday personal devices and sprawling hardware farms into invisible engines of synthetic traffic. In this third installment of the Adprodex Historical Observatory, we analyze how the surge in malicious apps, physical click farms, and SDK spoofing drained billions from marketing budgets, exposing that a mobile click rarely originated from a living human finger.
The Official App Store Scandal: Over 600 Million Infected Downloads
The most alarming revelation of 2019 was that these widespread ad scams were not distributed via shady websites or illicit downloads, but directly through the official Google Play Store and Apple App Store, routinely approved and certified by security review systems. Joint investigations by investigative outlets like BuzzFeed News alongside cybersecurity leaders such as Check Point and Kochava exposed shocking operations, notably that of developer DO Global (partially owned by Chinese internet giant Baidu): roughly 100 everyday utility apps, racking up over 600 million cumulative downloads, harbored secret code programmed to generate non-stop fraudulent ad clicks behind the backs of users and advertisers.
The Trojan Horse: How Apps Outsmarted Google and Apple Security
How could Silicon Valley giants repeatedly greenlight fraudulent software? The technique was deceptively simple: during app submission and automated store review, the application was completely clean and complied with all platform policies. Only after being installed onto the user's smartphone did the app receive remote instructions from command servers or activate dormant ad SDK payloads. The malware operated on a time delay, predominantly while the phone was locked, charging, and with the screen completely off: the devices secretly rendered invisible background ads and videos, draining battery life and mobile data to collect advertiser payouts at the expense of marketing budgets.
From Software Code to Warehouses of Bots: Physical Click Farms
Alongside covert app malware, 2019 brought public awareness to the industrial scale of physical click farms: sprawling warehouse facilities housing hundreds of thousands of actual smartphones mounted on metal racks, governed by centralized automation software. These hardware farms were rented out to artificially manipulate app rankings, fabricate install metrics (app install fraud), and mimic complex user journeys. To legacy ad platforms, traffic originated from authentic physical hardware with valid device fingerprints, making traditional fraud filters utterly useless.
The Breakdown of Mobile Attribution: Click Injection and Flooding
Historical data aggregated by our Observatory reveals that 2019 cyber tactics strategically hijacked attribution models—the algorithms deciding which marketing channel gets credited and paid for a conversion. Through click injection (transmitting a synthetic click milliseconds before a genuine user finishes downloading an app) and click flooding (spraying millions of phantom clicks hoping to match an organic install), fraudulent networks captured billions in performance advertising budgets, enriching bot syndicates instead of authentic marketing partners.
Today's Strategic Reality: The Open Mobile Web Remains a Bottomless Pit
Reflecting on 2019 provides essential clarity for contemporary advertising decisions. Brands and businesses that continue paying for open mobile display or in-app programmatic banners inherit these identical systemic vulnerabilities, today amplified by machine learning and automated bots. Measuring campaign success solely via virtual metrics and platform dashboards subjects advertisers to relentless financial waste benefiting opaque intermediaries.
The Radical Adprodex Solution: Closing the Ecosystem
The proprietary architecture behind Adprodex and the Tyche App was conceived specifically as an antidote to open mobile advertising failures. We eliminated third-party ad SDKs and pop-up banners entirely. Attention is locked at 100% through mandatory 12-second video spots, shielded by rigorous OTP anti-bot verification. Crucially, business value is not measured in phantom clicks or fake downloads, but by the physical presence of verified customers inside your local business validated through secret PIN codes. Anchoring ad investment to human-to-human transactions permanently eliminates digital bot fraud.
Ready to protect your company from mobile ad fraud?
Stop paying for phantom clicks and background impressions. Experience absolute transparency and verified foot traffic through Adprodex's closed ecosystem.